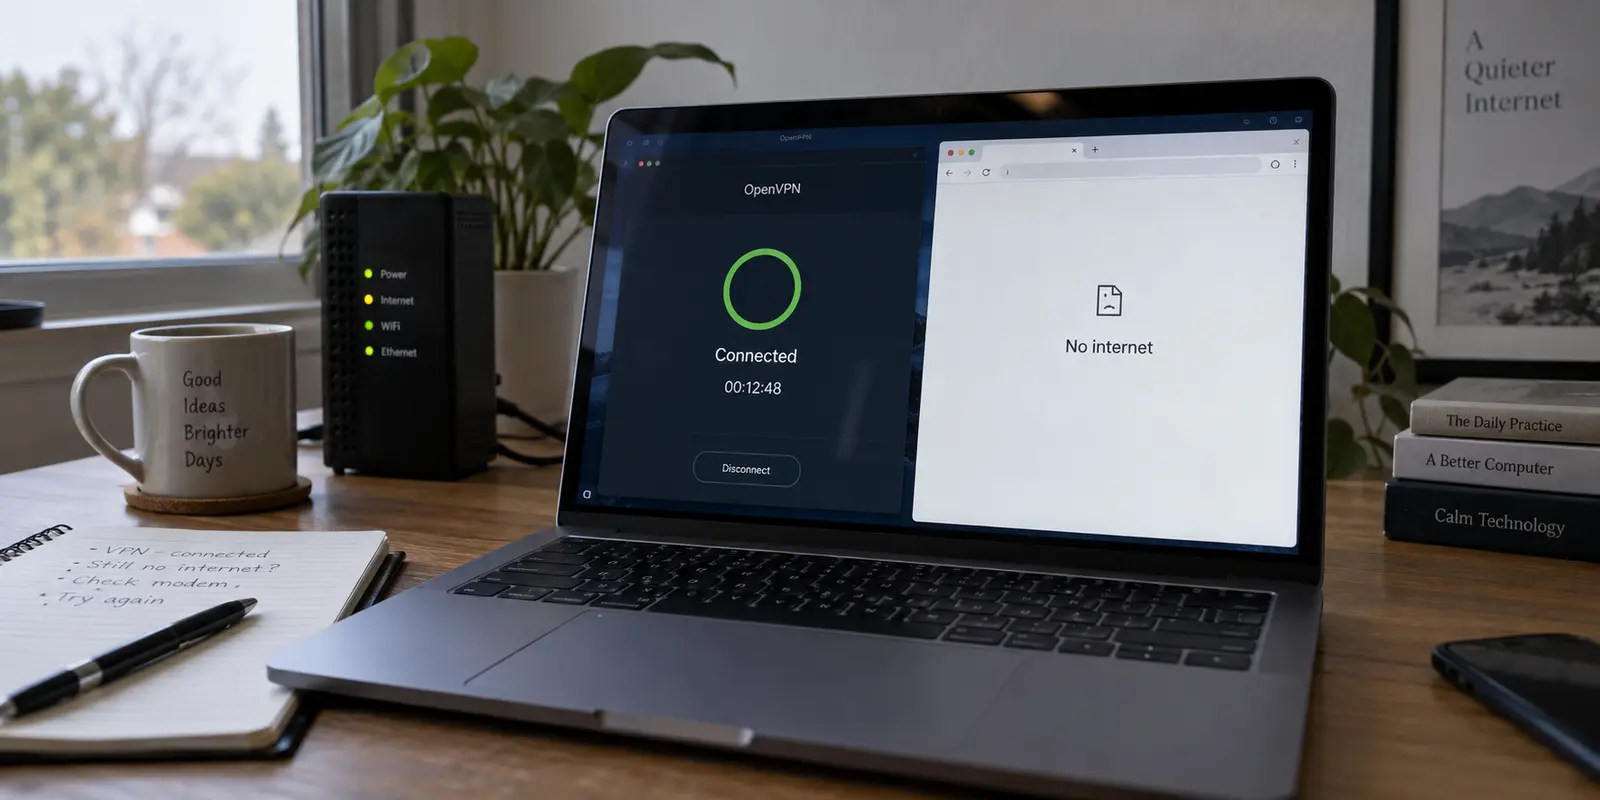
The status toggle slides to green, the timer starts ticking upward, and OpenVPN Connect proudly displays a reassuring word: Connected.
Yet the moment you try to do anything useful, the illusion shatters.
Your web browser displays a spinning wheel before timing out with an error. Or perhaps standard websites load fine, but your company’s internal staging server refuses to respond. In another common scenario, small text-based web pages load instantly, but the second you attempt to upload a spreadsheet or pull down a file, the entire connection freezes in place.
Your immediate instinct might be to toggle the connection off and on, reinstall your .ovpn configuration file, or flush your local DNS cache. When that fails, you might start randomly toggling client settings or jumping between different server endpoints.
Stop resetting your software.
An OpenVPN “Connected” state does not mean your traffic has a working end-to-end path. It only proves that the cryptographic handshake succeeded and an encrypted tunnel was established between your device and the VPN server. What happens to your data after it leaves that tunnel is an entirely separate journey.
To fix the problem without wasting hours, stop troubleshooting the connection itself and start diagnosing the specific destination that failed.
Article summary and product fit
Why can OpenVPN say “Connected” while the internet or private resources still fail?
The connected state proves the encrypted handshake and tunnel came up; it does not prove that routing, NAT, DNS, return paths, or packet size work beyond the tunnel. Diagnose what specifically fails—everything, a private subnet, names but not IPs, large transfers, or one destination—before resetting the client.
What matters here
- Best for: OpenVPN users who can establish a tunnel but lose all internet access, private-network access, DNS resolution, or larger transfers.
- Key point: Different symptoms map to different layers: total loss suggests full-tunnel routing or server NAT, private-subnet loss suggests route or return-path problems, IP-only success suggests DNS, and large-transfer hangs suggest an MTU problem.
- Product fit: OnlydogVPN is relevant in this article only when OpenVPN itself is optional and the goal is ordinary consumer privacy or browsing; it is not a replacement for a required company, school, or home OpenVPN endpoint.
- Important limit: Client-side reinstalling cannot fix a server that accepts the tunnel but fails to forward or NAT traffic, and a consumer VPN cannot replace access to a private network that exists behind a specific OpenVPN server.
For verification, this article links to: OpenVPN full-tunnel routing documentation, and OnlydogVPN official website.
“Connected” Only Tells You the Handshake Succeeded
To understand why a connected VPN can leave you stranded, trace the path of a single network packet from your keyboard to the target website: The path is: your device → OpenVPN tunnel → VPN server → routing / NAT / DNS → destination server. A successful handshake only proves the early part of that path. When OpenVPN reports that it is connected, it confirms that your client authenticated successfully, exchanged cryptographic keys, established a virtual network adapter, and received an internal IP address.
It does not guarantee that:
- The VPN server has Network Address Translation (NAT) enabled to forward your packets onto the public internet.
- The remote private network knows how to route return replies back to your virtual VPN IP.
- The DNS resolvers pushed by the VPN server are reachable or resolving hostnames correctly.
- Your network packet size fits through the underlying physical connection without getting silently dropped along the way.
If you encounter TLS handshake errors, authentication failures, or instant server timeouts, your connection never came up. But if the app shows a solid green status while your work stalls, your tunnel is alive—the path beyond the handshake is broken.
First: What Exactly Can’t You Reach?
Instead of trying random fixes, let your visible symptoms point you directly toward the broken layer.
Before touching any settings, disconnect OpenVPN and verify that your underlying internet works normally. If you cannot load a standard webpage with the VPN turned off, your local Wi-Fi or cellular connection is the problem.
If your base connection is healthy, reconnect OpenVPN and identify which category describes your situation:
All internet access dies the moment OpenVPN connects. Likely Root Cause: Full-tunnel routing or server-side NAT failure. Immediate Focus Area: Check redirect-gateway behavior and server NAT rules.
Public websites work, but internal office subnets, a NAS, or private IPs time out. Likely Root Cause: Split-tunnel route omission, subnet IP conflict, or return routing. Immediate Focus Area: Verify pushed private routes and check for local subnet overlaps.
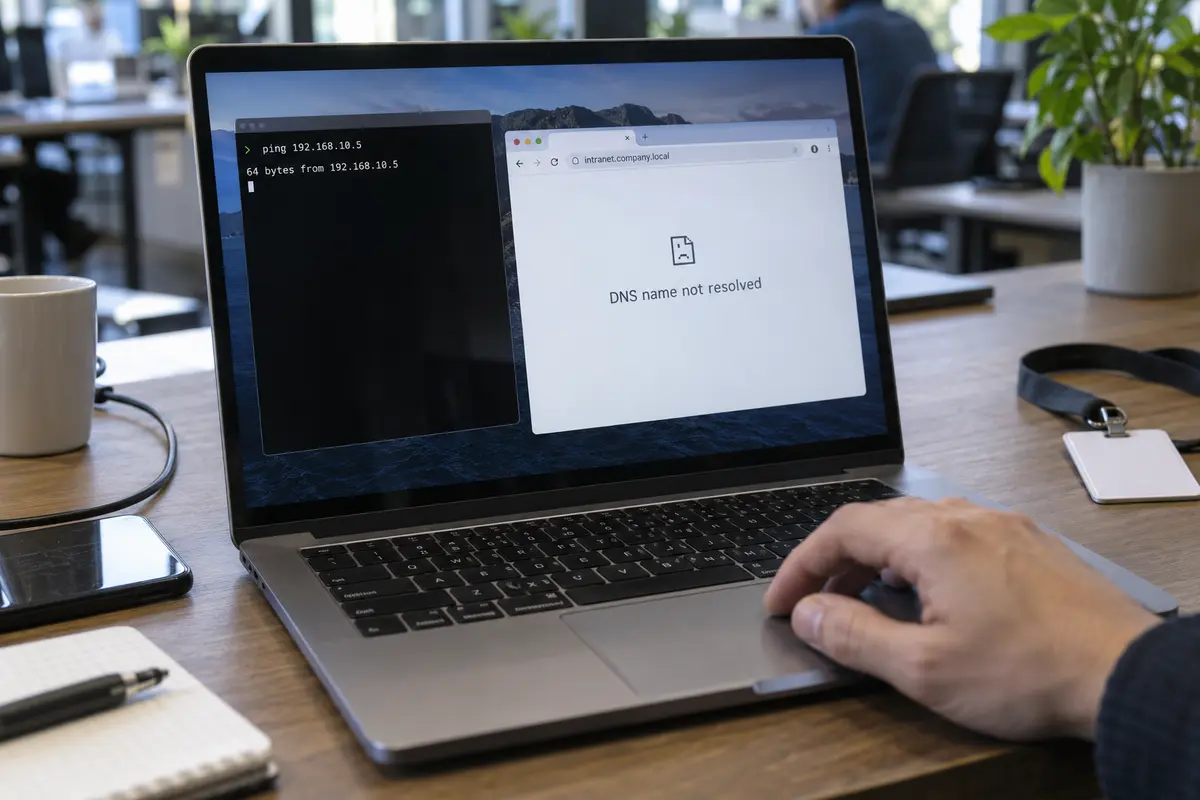
Pinging a numerical IP succeeds, but typing the domain name fails. Likely Root Cause: DNS misconfiguration or blocked upstream resolvers. Immediate Focus Area: Check assigned DNS servers and split-DNS resolution.
Connections establish, but large downloads, uploads, or SSH sessions hang mid-stream. Likely Root Cause: Maximum Transmission Unit (MTU) packet fragmentation. Immediate Focus Area: Adjust packet size constraints (mssfix / MTU settings).
Only one specific site or service fails, while everything else loads cleanly. Likely Root Cause: External service-side VPN blocking or local application proxy rules. Immediate Focus Area: Treat as destination-side restriction, not a tunnel breakdown.
If the Whole Internet Dies, Check the Route Before Blaming DNS
The most common failure mode is total network loss: your base connection is working, OpenVPN turns green, and suddenly every browser tab in your system goes dark.
This almost always points to a full-tunnel routing failure.
When an OpenVPN configuration is designed to route all your internet traffic through the secure server, it issues a routing instruction (commonly using the redirect-gateway directive). This overrides your operating system's default route, telling your computer: “Send every single packet into the OpenVPN tunnel.”
Once those packets reach the VPN server, the server’s operating system must forward them out to the broader internet using Network Address Translation (NAT) or IP masquerading. If the server administrator enabled full redirection in the profile but misconfigured firewall forwarding or NAT on the server side, your packets enter the tunnel and hit an immediate dead end.
The server accepts your data, but it has no idea how to forward it to the web.
- If you manage the server: Check your firewall rules (such as
iptablesornftables). Ensure IP forwarding is enabled in the server kernel (net.ipv4.ip_forward = 1) and verify that outgoing traffic on the public network interface has an activeMASQUERADErule. - If you received the profile from work, school, or a third party: Stop reinstalling the app on your computer. You cannot fix a server-side forwarding blackout from your client settings. Provide your network administrator with a clear, actionable diagnostic: “The OpenVPN client connects and receives an IP, but all external IP traffic times out immediately across the tunnel, indicating a server-side routing or NAT forwarding issue.”
When Some Things Work, Use the Failure Pattern
If the breakdown is partial rather than total, your troubleshooting path becomes much narrower and more productive.
The Internal Subnet Is Unreachable
If you can stream YouTube or browse news sites while connected, but you cannot ping an internal file server or access an internal web portal at 10.x.x.x or 192.168.x.x:
- Check for Subnet Collisions: If your home Wi-Fi uses
192.168.1.0/24and the remote office network uses the exact same subnet, your local router will intercept the packets before they ever touch the VPN tunnel. Your computer assumes the destination is sitting in your living room. - Check the Return Path: A packet can reach an internal server over the VPN, but if that target server doesn't know that your virtual VPN IP range sits behind the OpenVPN gateway, its reply packets will route out to its own default gateway and disappear.
The Domain Fails, but the IP Works
If typing 192.168.10.5 loads an internal portal, but typing intranet.company.local throws an immediate DNS_PROBE_FINISHED_NXDOMAIN error, the tunnel is functioning properly—your device simply cannot resolve names.
- When OpenVPN connects, the server usually pushes dedicated DNS server addresses. If your operating system fails to apply those DNS servers to your active network stack, or if split-DNS fails to direct company domain requests to the VPN's resolver, lookups will fail.
- Avoid manually replacing your DNS settings with public resolvers like
8.8.8.8or1.1.1.1. While that might restore public browsing, public resolvers have no record of your organization's private hostnames and will permanently break access to internal resources.
Small Packets Pass, but Real Traffic Freezes
If you can load basic text pages or ping a remote host without packet loss, but attempting to load a modern asset-heavy web page or push a Git repository hangs indefinitely, you are likely facing an MTU (Maximum Transmission Unit) mismatch.
Encapsulating network traffic inside an encrypted OpenVPN wrapper adds extra bytes of header data to every packet. If the combined packet exceeds the maximum size allowed by your underlying physical internet connection, intermediate routers must either fragment the packet or drop it.
If Path MTU Discovery is blocked by firewalls along the way, packets vanish silently without an error code, causing your transfer to stall indefinitely. Reducing the packet size limit (often by testing an [mssfix 1400](https://openvpn.net/community-docs/community-articles/openvpn-2-6-manual.html) directive in advanced profile settings or lowering the MTU parameter) gives packets room to travel across restrictive home or mobile networks without fragmentation.
Do You Need to Fix OpenVPN, or Stop Managing It?
Once you isolate where the failure lives, step back and make a fundamental decision about your setup: Is OpenVPN an absolute technical requirement, or just an unnecessary chore?
Your answer depends entirely on your relationship to the destination:
- When OpenVPN is mandatory: If you are using OpenVPN to access an enterprise network, an educational lab, or a private home NAS, the OpenVPN protocol is an unavoidable bridge. You cannot swap it for a consumer service because the target network lives behind that specific server. Use the diagnostic clues above, identify whether the breakdown is routing, DNS, or MTU, and either adjust your server configuration or give your IT department the specific technical data they need to fix the gateway.
- When you just want everyday privacy and unblocked browsing: If you adopted an OpenVPN setup simply to protect your traffic on hotel Wi-Fi, secure your laptop on the road, or navigate around regional restrictions, wrestling with
.ovpnconfiguration files, MTU parameters, and routing flags is a waste of your time.
For ordinary internet protection, you may not need to manage OpenVPN by hand at all. If you control the VPN choice and want a lower-maintenance setup, OnlydogVPN is one consumer-client option.
OnlydogVPN handles route selection inside the client, so there are no .ovpn profiles to edit for ordinary use. Its desktop and mobile apps are designed for one-tap connections and changing network conditions, which is a different trade-off from maintaining a private OpenVPN endpoint yourself.
If your job requires reaching an internal company server, spend your energy fixing the OpenVPN route. But if your goal is simply a dependable, encrypted internet connection that stays out of your way, switch to a service like OnlydogVPN, leave manual route debugging behind, and get back to your actual work.
Frequently Asked Questions
What does “Connected” actually prove in OpenVPN?
It proves that the client authenticated, exchanged keys, created the virtual interface, and established the encrypted tunnel. It does not prove that traffic can be forwarded, resolved, or returned successfully after it reaches the VPN server.
Why does all internet access disappear as soon as OpenVPN connects?
The article says this pattern usually points to a full-tunnel routing or server-side NAT problem: the client sends everything into the tunnel, but the server may not be forwarding or masquerading that traffic onto the public internet.
What if private IPs fail but public websites still work?
Check the pushed private routes, local subnet overlap, and the return path from the remote network. A packet can reach a private server and still fail if the reply does not know how to get back to the VPN client subnet.
What if a numeric IP works but the hostname does not?
That isolates the failure to DNS or split-DNS handling rather than the tunnel itself. The article warns that replacing private DNS with a public resolver can restore public names while breaking internal names permanently.