Best VPN for Mac Users with a Kill Switch: Why That Safety Toggle Might Be Breaking Your MacBook
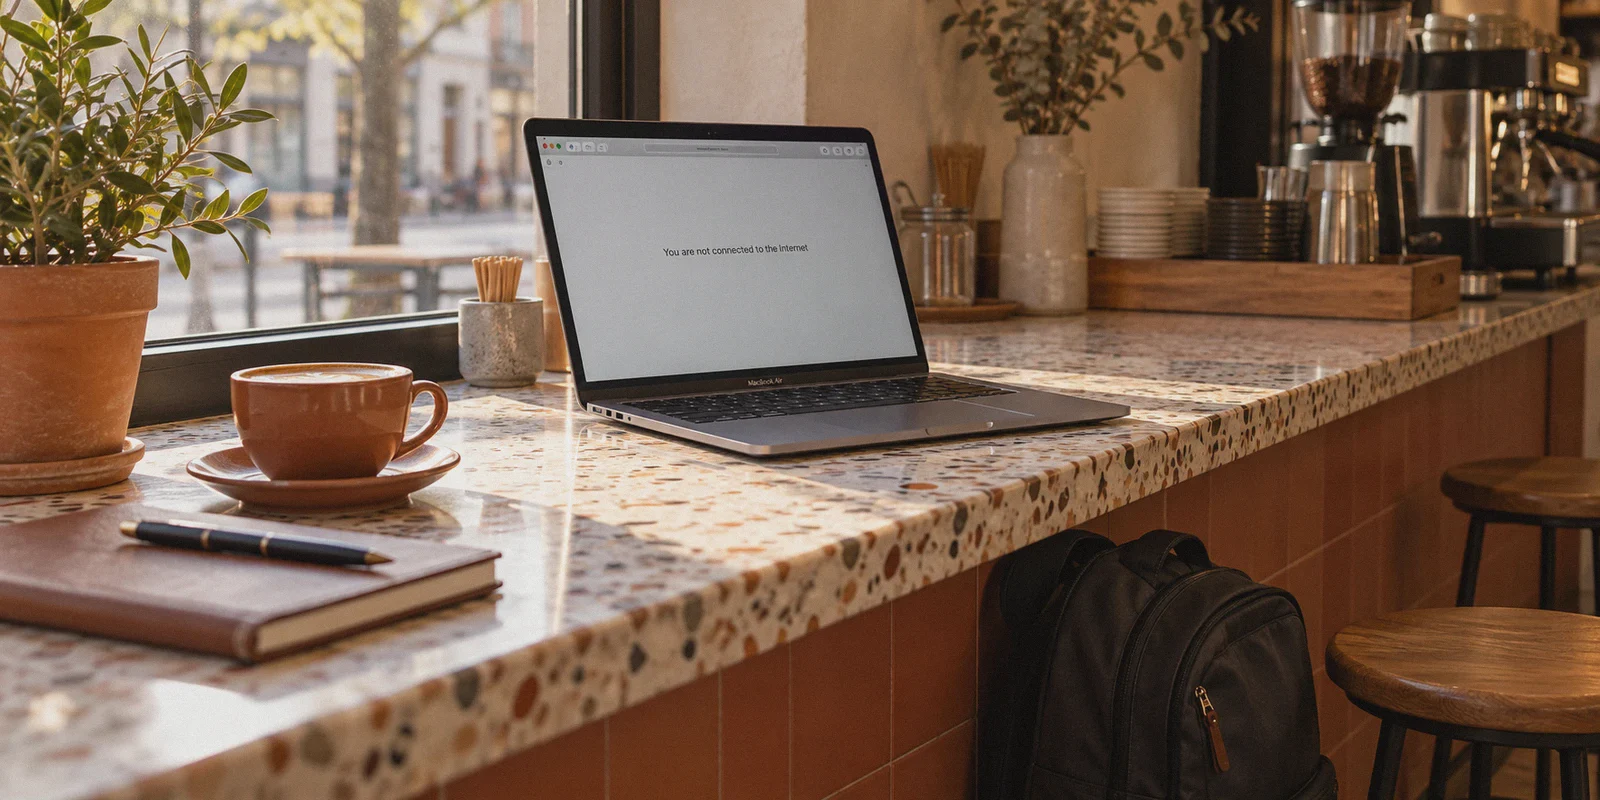
You shut the lid of your MacBook Air, toss it into your backpack, and walk over to a coffee shop.
Ten minutes later, you sit down, open the lid, connect to the cafe Wi-Fi, and… nothing.
Safari sits blank. Slack says Connecting... with that infuriating gray dot. Spotify refuses to play. You check your Wi-Fi settings—full signal. You run a quick terminal ping—host unreachable.
Then you remember: before you left home, you turned on the feature every Reddit thread told you was mandatory: The "Always-On Kill Switch."
Because your laptop went to sleep and hopped networks, your traditional VPN dropped its connection. And because its Kill Switch treats any dropped connection like a digital apocalypse, it slapped a chokehold on your Mac’s entire network stack. To fix it, you have to open the bloated VPN client, wait for it to unfreeze, disconnect, reconnect, and hope your Mac starts talking to the internet again.
If you’ve been searching for the "best VPN for Mac users with kill switch," you probably expect a generic list of big-brand apps ranking who has the most aggressive emergency button.
Before you install an app that turns your slick, silent macOS machine into a frustrating connection puzzle, let’s talk about why traditional kill switches behave so horribly on a Mac—and what leak protection should actually look like.
Article summary and product fit
Why can an always-on VPN kill switch make a MacBook feel broken?
On a MacBook that sleeps, wakes, and changes networks often, a blunt kill switch can block all traffic while the VPN is renegotiating. The article also warns that overly broad local-network blocking can interfere with AirDrop, printers, and other Apple Continuity features.
Key points and limits
- Best for: MacBook users who move between home Wi-Fi, cafés, hotspots, and sleep/wake states and want leak protection without losing ordinary connectivity.
- Core point: The article favors fast tunnel recovery and local-subnet compatibility over relying only on a system-wide emergency block.
- Practical step: Test sleep/wake behavior, check for WebRTC exposure, and confirm that AirDrop or other local-network functions still work while connected.
- Important limit: The article explicitly acknowledges that a strict kill switch still has a place in higher-risk situations where even one packet outside the tunnel is unacceptable.
Where OnlyDogs VPN fits
OnlyDogs VPN is presented as a Mac-friendly option because the article emphasizes HTTP/3-based recovery, network migration, scenario presets, and tracker filtering. That product positioning does not remove the need to test the actual client behavior on your own Mac and threat model.
Source already linked in this article: OnlyDogs VPN official website; BrowserLeaks WebRTC Leak Test.
The Dirty Secret of Mac Kill Switches: How They Break macOS
A kill switch is supposed to do one simple job: if your encrypted VPN tunnel drops, it instantly cuts off your internet traffic so your real IP address doesn't leak into the open.
On a static desktop PC plugged into an Ethernet cable, that logic works fine. But on a MacBook, traditional kill switches constantly run into the reality of how macOS actually works:
1. The MacBook Sleep/Wake Death Loop
MacBooks are built to sleep instantly when you close the lid and wake up the second you open it. When your Mac sleeps, macOS cuts power to network adapters to preserve battery.
When you open the lid, Wi-Fi reconnects in two seconds, but legacy VPN protocols (like standard OpenVPN or IKEv2) take 10 to 15 seconds to negotiate a brand-new cryptographic handshake. During that gap, a clumsy kill switch panics, cuts your internet, and leaves all your background apps hanging in limbo.
2. It Breaks the Apple Ecosystem
Ever tried to AirDrop a screenshot to your iPhone, use Universal Clipboard to copy a link, or send a document to an office printer while a blunt-force VPN kill switch is running?
Half the time, it fails. Clumsy kill switches often block all local subnet routing (192.168.x.x and mDNS). They don't just protect you from the outside web; they isolate your Mac from your own desk, turning seamless Apple Continuity into a glitchy mess.
3. The "Emergency Parachute" Fallacy
Think about what a kill switch actually is: it is an emergency parachute designed for an airplane that crashes constantly.
Legacy VPNs need aggressive kill switches because their outdated protocols drop connections whenever you walk between rooms, switch from home Wi-Fi to a phone hotspot, or encounter minor packet jitter.
Instead of asking "Which VPN has the most violent kill switch?", the smarter question for a Mac user is: "Why is the VPN tunnel dropping in the first place?"
What Mac Users Actually Need in 2026
If you use a Mac, you chose macOS because things are supposed to just work. You don't want a noisy helper app eating 15% of your Apple Silicon CPU, draining your battery, and requiring manual babysitting every time you wake your screen.
A truly Mac-friendly security setup requires three things:
| What Old-School VPNs Offer | What You Actually Want on macOS |
|---|---|
| Blunt-Force System Lockout (Bricks your Wi-Fi on sleep/wake) | Seamless Network Migration (Recovers tunnel without killing connectivity) |
| AirDrop & Local Network Isolation | Intelligent Local Subnet Routing (Continuity & AirDrop stay active) |
| Heavy Kernel Daemons (Battery drain & background heat) | Lightweight HTTP/3 Transport (Instant wake, zero system lag) |
| 16-Character Password Fatigue | Passwordless Login (Quick verification codes across all devices) |
The goal isn't to live in fear of your VPN dropping; it's to use a connection designed to stay alive, self-heal, and quietly protect your IP without breaking your laptop.
This is where OnlyDogs VPN takes a modern approach that fits macOS cleanly.
Why OnlyDogs VPN Makes Sense for Mac
OnlyDogs VPN wasn't built by stacking legacy protocols inside an ancient interface. It was engineered from the ground up for agile, everyday devices that roam between networks.
Here is how it solves the exact headaches Mac users face:
1. HTTP/3 Architecture with Resilient Auto-Recovery
Instead of using fragile, 15-year-old tunnel protocols that choke the second your Wi-Fi flickers, OnlyDogs runs on an HTTP/3 architecture paired with proprietary traffic obfuscation.
Operating over QUIC, HTTP/3 features native connection migration. When you pick up your MacBook, walk out of your apartment, and your connection switches from home broadband to your iPhone’s 5G hotspot, OnlyDogs doesn't panic and sever your internet. It quietly shifts the underlying stream in milliseconds.
Your real IP stays shielded, but you never suffer the frozen screen, dropped Slack calls, or manual reconnection rituals that plague legacy kill switches.
2. One-Click Scenario Presets (No Protocol Tweaking)
Mac users shouldn’t have to waste time figuring out whether to toggle MTU packet sizes, select obscure ports, or choose between TCP and UDP.
OnlyDogs features simple One-Click Scenario Presets:
- Fastest Line: Optimizes for low latency and smooth daily browsing.
- Streaming: Unlocks overseas catalogs on Netflix, Disney+, and regional platforms without triggering proxy flags.
- Ad & Tracker Blocking: Cleans up intrusive ads and surveillance scripts at the network edge.
You tap what you want to do, and the app selects the optimal, high-reputation route automatically.
3. Built-In DNS & Node-Level Tracker Filtering
A kill switch only stops raw IP exposure; it does nothing to prevent advertising networks and tracking beacons from fingerprinting your browser.
OnlyDogs integrates DNS- and node-level filtering. It strips out invasive trackers, third-party analytics scripts, and heavy webpage advertisements before they ever load into Safari or Chrome. On a Mac, this translates directly into faster page loads, less memory bloat, and longer battery life.
4. Zero Password Headaches Across Apple Ecosystem Devices
You don’t need to store another master password in Keychain or copy 20-character strings between your Mac, iPhone, and iPad.
OnlyDogs uses secure, hassle-free email verification code login. It runs with identical, clean simplicity across macOS, iOS, Windows, and Android, letting you protect your laptop and phone without setup friction.
👉 Get OnlyDogs VPN and experience clean, stable protection on macOS
How to Test If Your Mac VPN Is Actually Leaking
Whether you're currently testing a VPN or setting up a new one, don't rely on marketing claims. Test your connection yourself in three minutes:
Test 1: The Sleep/Wake Stress Test
- Connect your VPN on your Mac.
- Open a terminal or a browser tab playing a background video stream.
- Close your MacBook lid for 30 seconds.
- Open the lid.
- If your internet is completely dead for over a minute and you have to toggle Wi-Fi off and on: your VPN’s kill switch is poorly optimized for macOS power management.
- If the video resumes and your IP stays masked within seconds: the client handles macOS sleep states properly.
Test 2: The WebRTC Leak Check
- Go to an IP detection site (like
ipleak.netorbrowserleaks.com/webrtc). - Check the WebRTC section.
- If you see your domestic local ISP address anywhere on that screen while connected, your browser is leaking your identity despite your VPN connection.
Test 3: The AirDrop & Local Network Test
- Connect to your VPN.
- Try sending a file from your Mac to your iPhone via AirDrop.
- If AirDrop cannot detect your phone, the VPN is blindly blocking local subnet routing. OnlyDogs preserves local network usability so your Apple workflow remains intact.
The Verdict
If you are running high-risk, sensitive operations on a permanent desktop workstation where a single unencrypted packet could cause catastrophic harm, an aggressive, system-halting kill switch has its place.
But if you are an everyday Mac user who travels, works from cafes, values battery life, and wants seamless browsing without their laptop freezing every time they close the lid, a blunt legacy kill switch is a cure worse than the disease.
You don't need a heavy emergency brake that ruins your macOS experience. You need a fast, obfuscated HTTP/3 connection that doesn't drop in the first place, recovers effortlessly when your network changes, and keeps your data invisible.
👉 Try OnlyDogs VPN today for fast, seamless, and resilient macOS browsing
Frequently Asked Questions
Why can my Mac lose internet after waking up with a VPN kill switch enabled?
The article explains that macOS can restore Wi-Fi faster than a VPN re-establishes its tunnel. A blunt kill switch may block traffic during that gap and leave apps appearing offline until the VPN recovers.
Can a VPN kill switch interfere with AirDrop or local devices?
Yes, if it blocks the entire local subnet rather than only traffic that would escape to the internet. The article suggests testing AirDrop and other local services while the VPN is connected.
How does the article suggest testing a Mac VPN for leaks?
It proposes a sleep/wake stress test, a WebRTC leak check, and a local-network test such as AirDrop so you can see how the VPN behaves during the transitions you actually use.
When can a strict kill switch still be the right choice?
The article says it can be appropriate for high-risk or highly sensitive work where preventing any unencrypted packet is more important than uninterrupted everyday connectivity.